> For the complete documentation index, see [llms.txt](https://docs.cloudeka.ai/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.cloudeka.ai/guideline-for-individual/deka-vpn/configuration-deka-vpn-ipsec/ipsec-tunnel/view-encryption-algorithm.md).

# View Encryption Algorithm

This page is used to view the encryption algorithms applied in the IPSec connection. The information displayed includes the encryption and hash algorithms used in both Phase 1 and Phase 2. There is steps to view Encryption Algorithm:

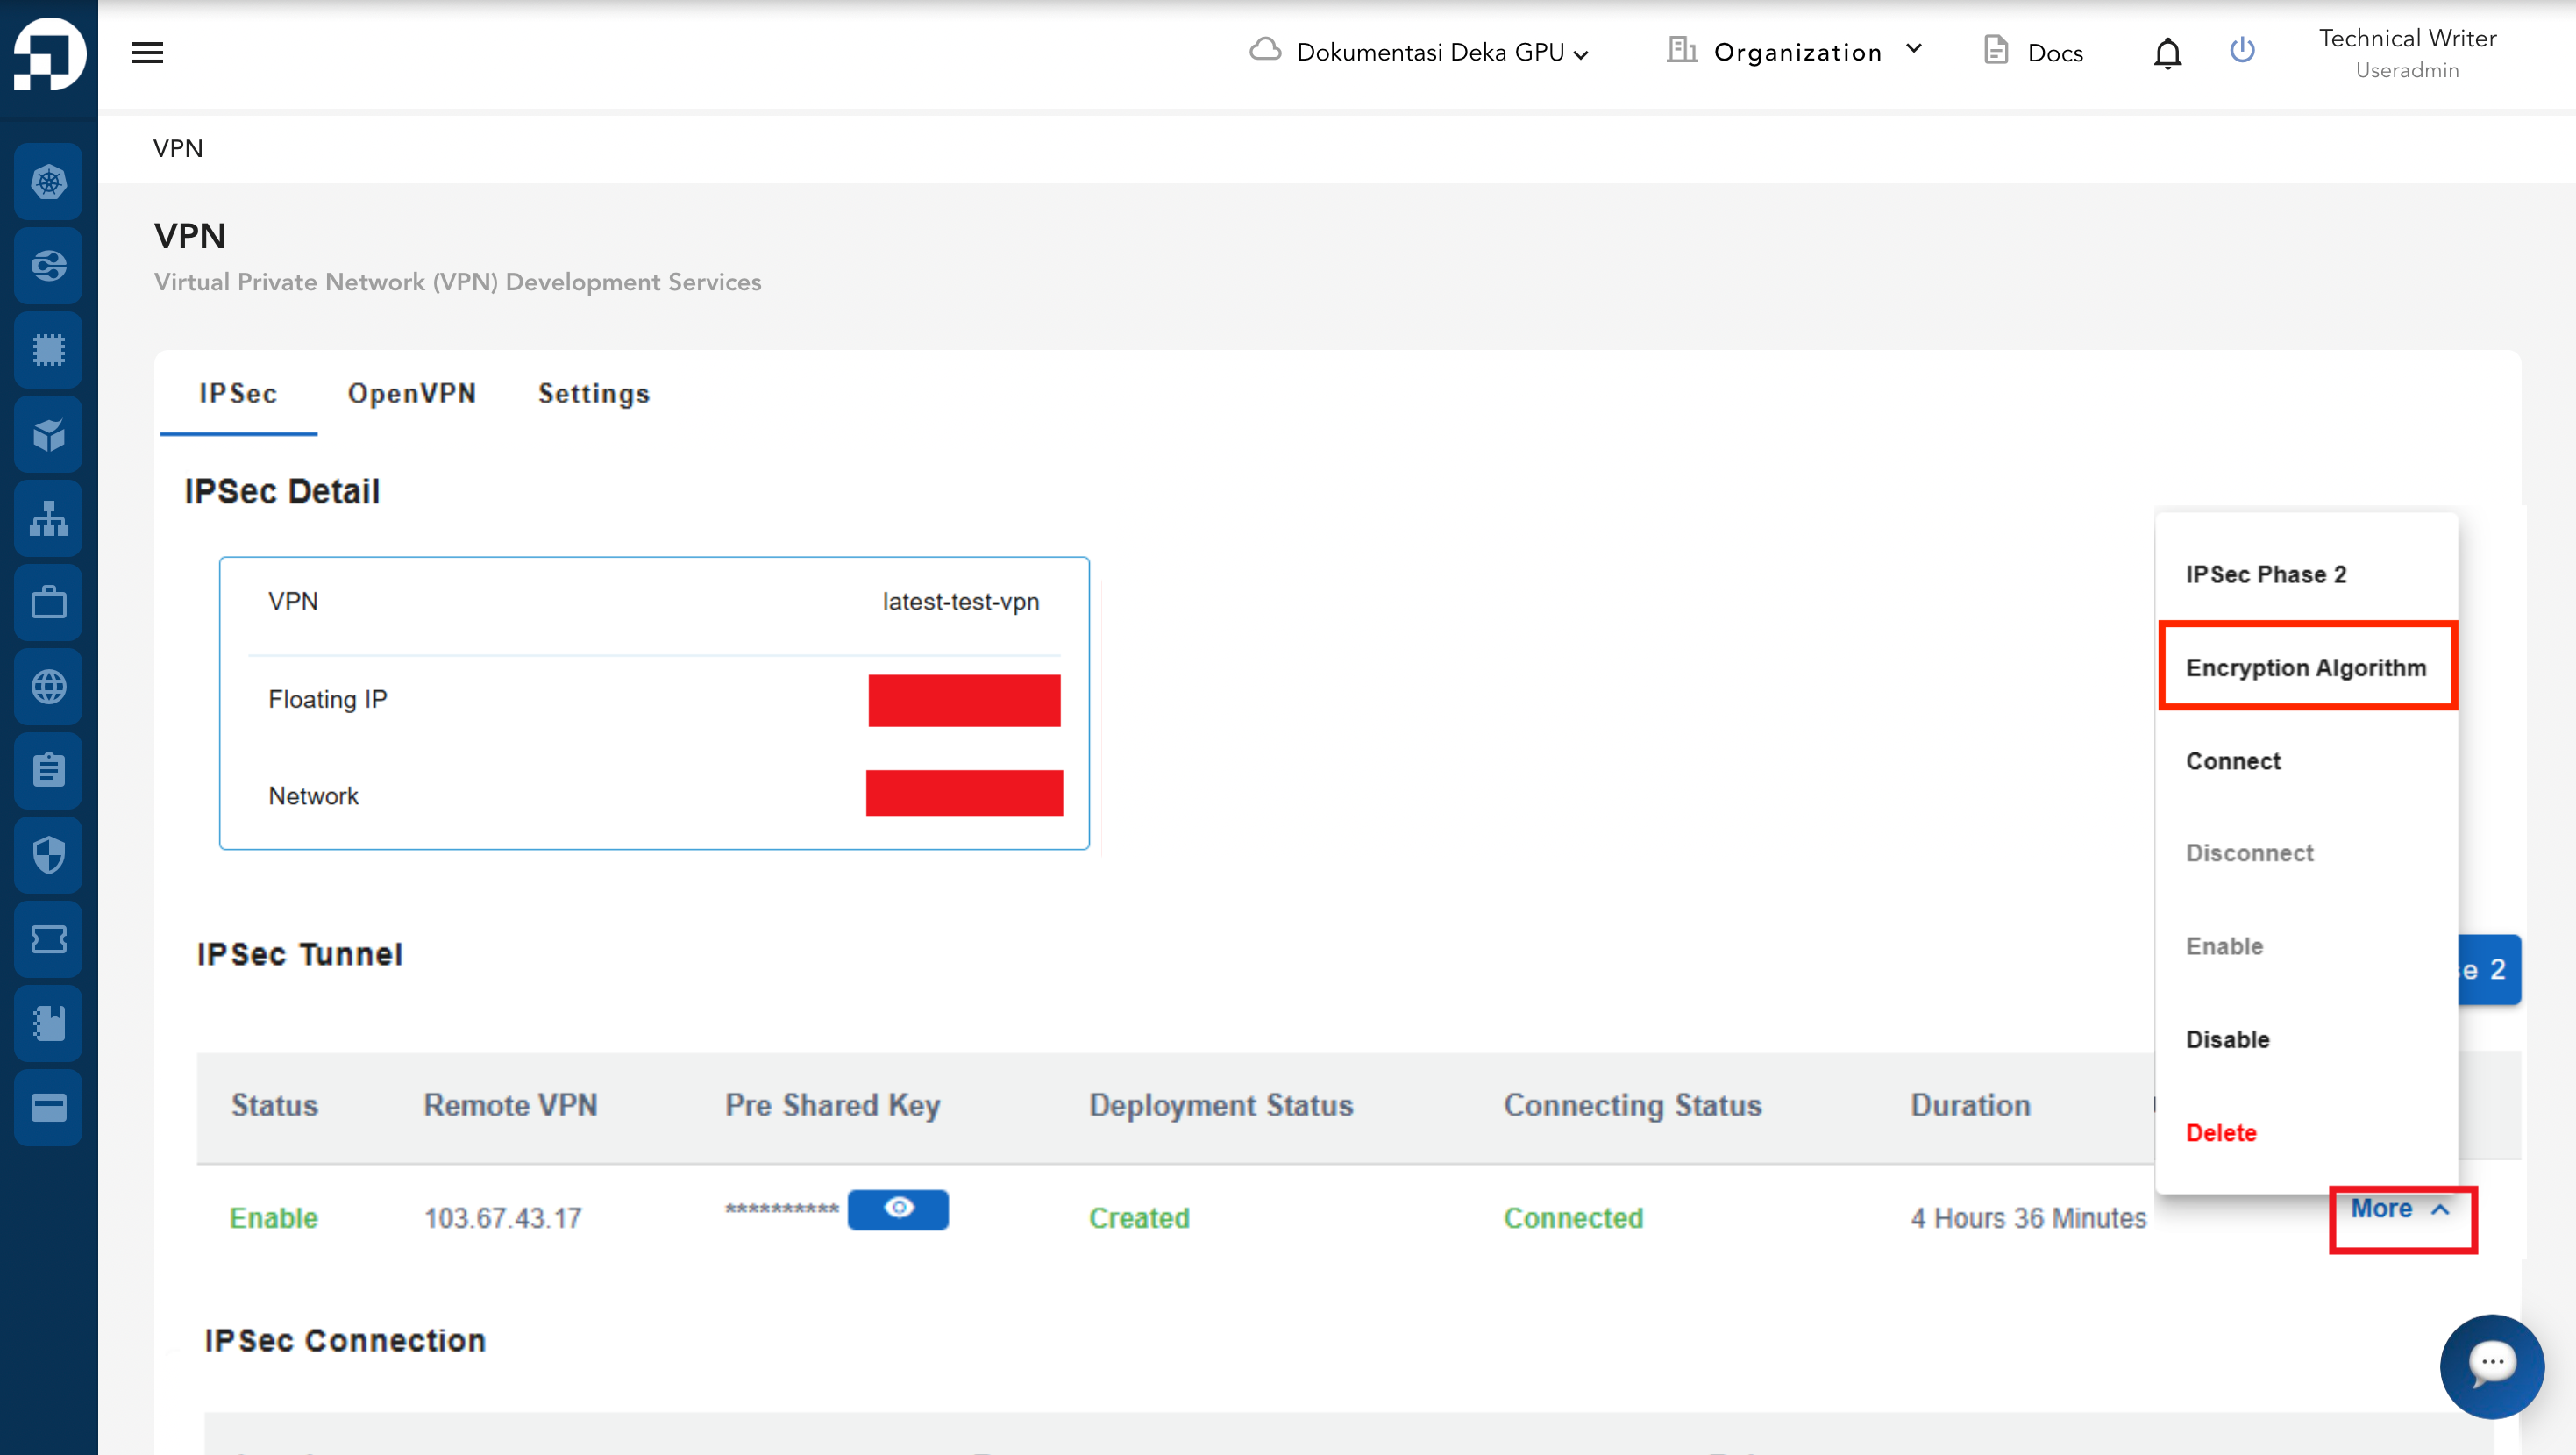
* From the **VPN** list, click **More → Configuration** on the selected VPN. In the **IPSec** tab, go to **IPSec Tunnel**, then click **More** on the tunnel row. Select **Encryption Algorithm**.

<figure><img src="https://content.gitbook.com/content/dRGHNSPw8ps5rkLJZT3A/blobs/xFQePKCu9OmjIa4mbVx1/image%20(6)%20copy.png" alt=""><figcaption></figcaption></figure>

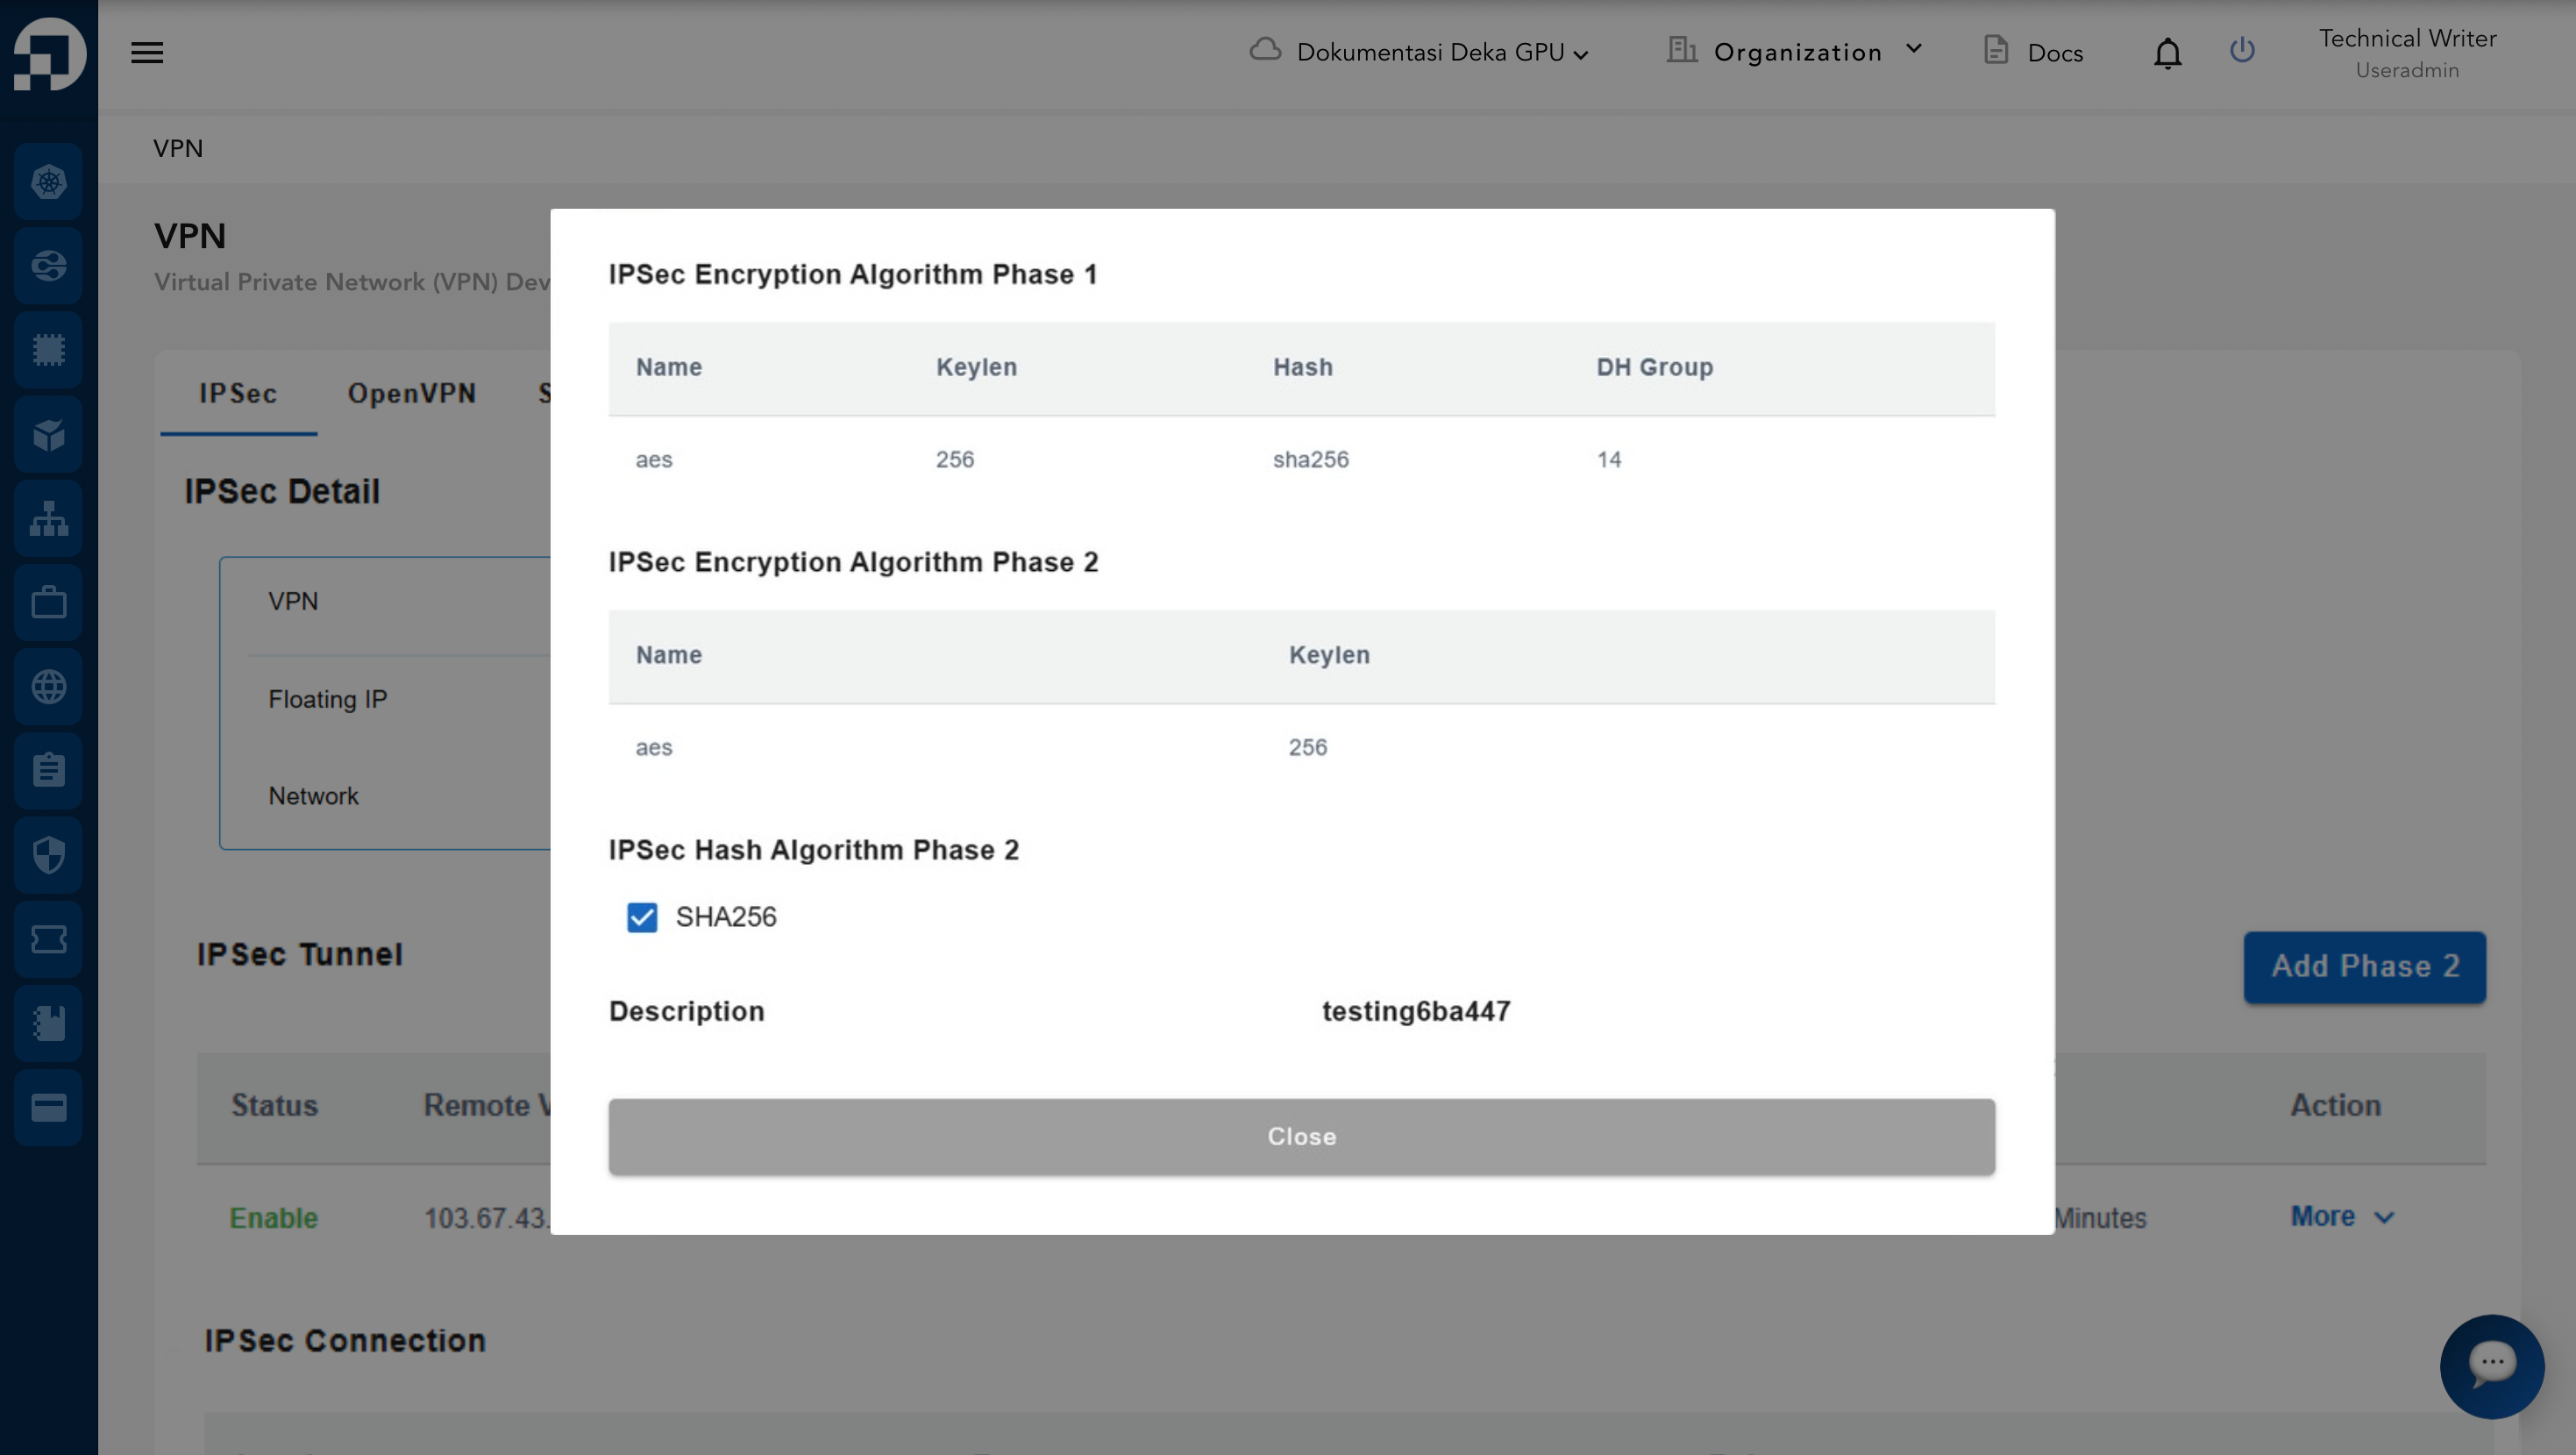
* The system will display a table with detailed information about the encryption and hash algorithms used in the IPSec connection.&#x20;

<figure><img src="https://content.gitbook.com/content/dRGHNSPw8ps5rkLJZT3A/blobs/p7N3812syKc7VKeE4U3Z/image%20(11).png" alt=""><figcaption></figcaption></figure>

The displayed information includes:

* **IPSec Encryption Algorithm Phase 1**

<table><thead><tr><th width="205.66668701171875">Column</th><th>Description</th></tr></thead><tbody><tr><td>Name</td><td>The encryption algorithm used (e.g., AES).</td></tr><tr><td><strong>Keylen</strong></td><td>The key length used (e.g., 256).</td></tr><tr><td><strong>Hash</strong></td><td>The hash algorithm for data integrity (e.g., SHA256).</td></tr><tr><td><strong>DH Group</strong></td><td>The Diffie-Hellman group used for key exchange (e.g., 14).</td></tr></tbody></table>

* **IPSec Encryption Algorithm Phase 2**

<table><thead><tr><th width="206.5">Column</th><th>Description</th></tr></thead><tbody><tr><td><strong>Name</strong></td><td>The encryption algorithm used (e.g., AES).</td></tr><tr><td><strong>Keylen</strong></td><td>The key length used (e.g., 256).</td></tr></tbody></table>

* **IPSec Hash Algorithm Phase 2** shows the selected hash method for Phase 2 (for example: SHA256).
* **Description** provides a short description or identifier of the configuration.
