> For the complete documentation index, see [llms.txt](https://docs.cloudeka.ai/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.cloudeka.ai/panduan-untuk-enterprise/cloudeka-api-list/command-reference/cldkctl-vpn/list-ipsec-phase2.md).
# list-ipsec-phase2
The vpn list-ipsec-phase2 command retrieves a list of IPSec Phase 2 configurations in your VPN. This command displays essential details such as Mode, Protocol, Status, Pfs Group, Lifetime, Local IP Subnet, Remote IP Subnet, and Description.
## Usage
```
cldkctl vpn list-ipsec-phase2 [flags]
```
## Steps
Follow the steps below to run and view the result of this command:
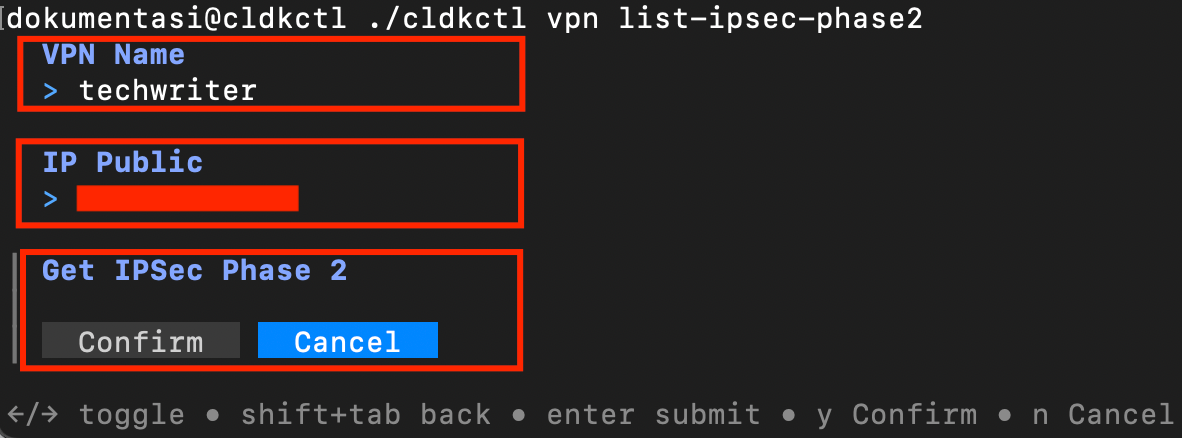
1. Run the following command in your terminal:
```
cldkctl vpn list-ipsec-phase2
```
2. Enter the VPN name in the **VPN Name** field. To obtain or verify it, refer to vpn list.
3. Enter the public IP address in the **IP Public** field.
4. Press **y** for Confirm or **n** for Cancel.
5. Once successful, the terminal displays the IPSec Phase 2 configuration list containing information such as Mode, Protocol, Status, Pfs Group, Lifetime, Local IP Subnet, Remote IP Subnet, and Description.
| Column | Description |
| ---------------- | --------------------------------------------------------------------- |
| Mode | The mode used for IPSec communication. |
| Protocol | Specifies the protocol used in the IPSec connection. |
| Status | Indicates whether the IPSec Phase 2 is enabled or disabled. |
| Pfs Group | Specifies the Perfect Forward Secrecy (PFS) group value. |
| Lifetime | Defines the key lifetime duration in seconds. |
| Local IP Subnet | Displays the local network range used for IPSec Phase 2. |
| Remote IP Subnet | Displays the remote network range connected through IPSec Phase 2. |
| Description | Provides an identifier or remark for the IPSec Phase 2 configuration. |
## Flags
{% hint style="info" %}
This command supports [global flags](/panduan-untuk-enterprise/cloudeka-api-list/global-flags.md). Refer to the Global Flags section for details.
{% endhint %}
| Flag | Description |
| ---------- | ------------------------------------ |
| -h, --help | Help for list ipsec phase 2 command. |